💼 Working adults›for IT professionals Reading·Intermediate
IT Technical Guidelines: Webhook Integration and Security Protocols
Technical documentation explaining how offshore software engineers handle webhook notifications, payload validation, and retry mechanisms for API integrations.
📖 Read the passage below
To obtain real-time notifications when a user generates custom profile records, offshore software engineers must define a webhook URL within the web tool. When a change occurs, the core program sends an HTTP POST request to a designated receiver. The payload is structured with JSON, containing fields such as the user ID, change kind, and creation timestamp.
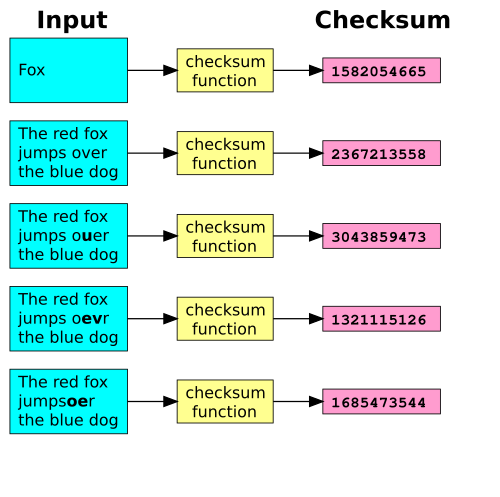
For payload genuineness, each transmission carries a cryptographic checksum embedded within the HTTP header. Offshore software developers compute a hash code using a custom passkey, matching numeric outputs before parsing payload fields. Requests showing mismatched checksums are dropped straightaway, thwarting forged packets.
When designated servers emit faults or stay silent over ten seconds, the delivery engine triggers retries. Retries follow an expanding interval scheme, making up to five retries across twenty-four hours. If all retries stall, delivery becomes paused, needing developer intervention through the web page.